FINANCIAL MODEL BASELINE CONTROL
Choose Model Baseline Access Modes
Map No Write, No Delete and No Access to each analyst, reviewer and Windows account.
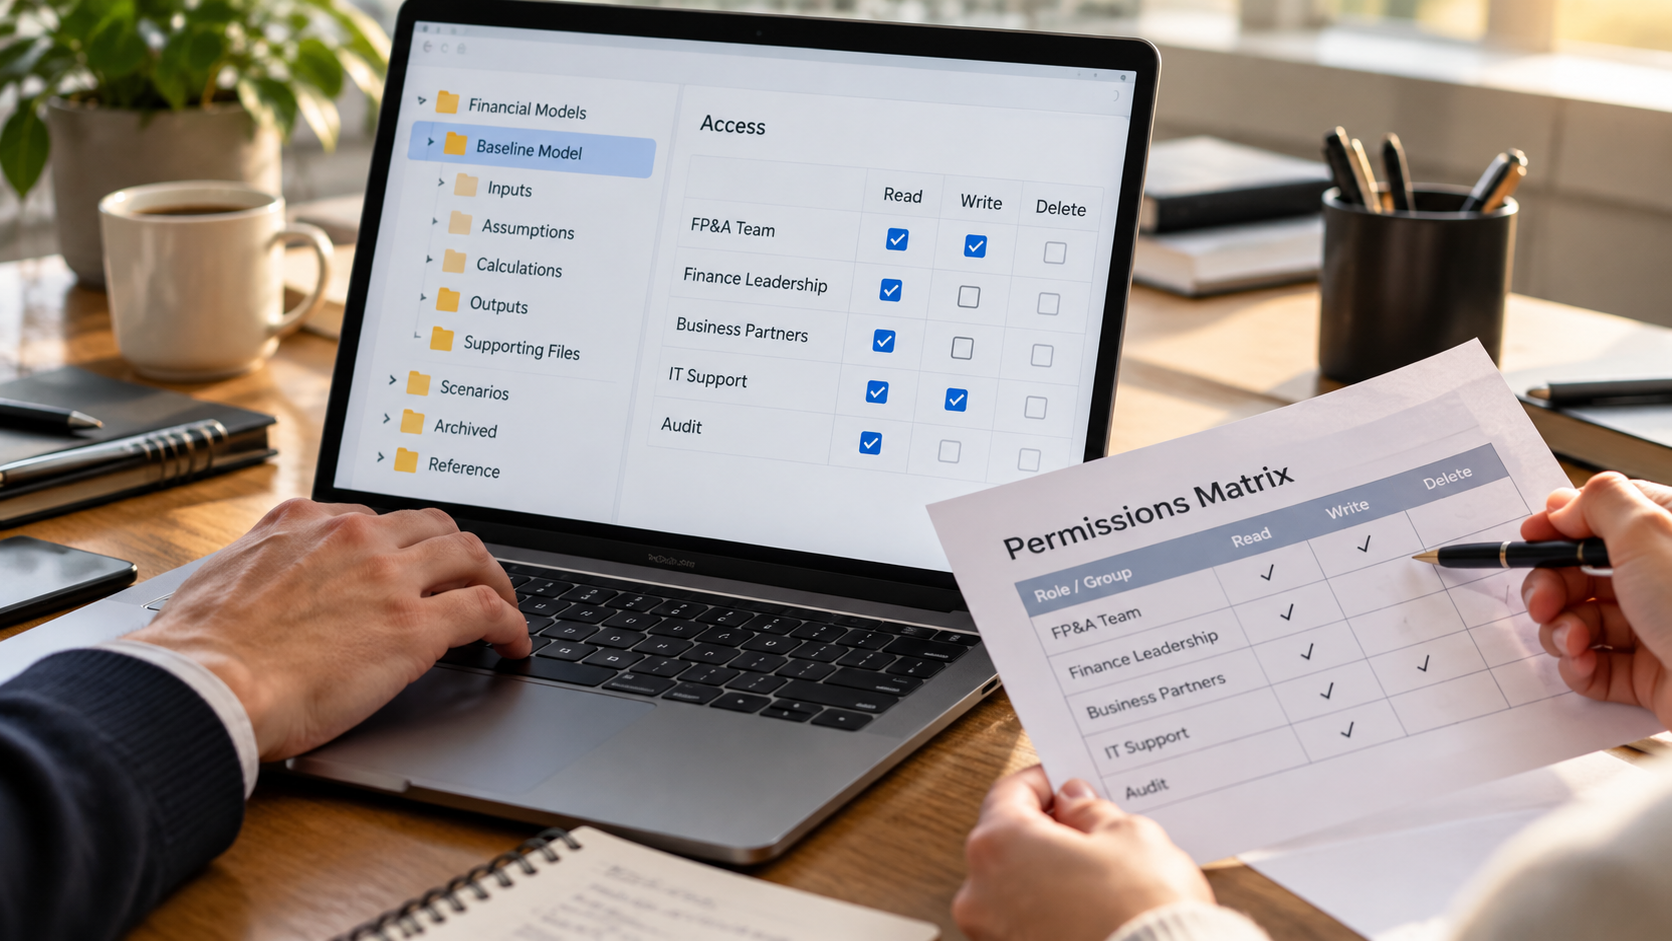
01 / CONTEXT
Define the control decision
The strongest restriction is not automatically the safest. Reviewers may need read access while the approved baseline must resist writing or deletion. Test each mode with the actual spreadsheet application, linked-data process and service accounts.
Map No Write, No Delete and No Access to each analyst, reviewer and Windows account.
02 / PROCEDURE
Run the control sequence
- 01
List every person and process that reads or writes the baseline.
- 02
Test No Write against the supported spreadsheet application.
- 03
Test No Delete without assuming it prevents copying or renaming.
- 04
Use No Access only when the workflow does not require reading.
- 05
Record the selected mode, exception and recovery owner.
03 / EVIDENCE
Preserve proof without personal data
A defensible control record identifies the model owner, planning period, scenario, currency, authoritative path, permitted accounts, restriction mode, version ID, approval date, checksum evidence, recovery owner and next review date. It should not contain confidential forecasts, live company figures, credentials or personal data. Use fictional entities and non-operational figures during every technical test.
Recheck the arrangement after changes to Windows, spreadsheet software, linked data, planning workflow, storage, Folder Protect, permissions, service accounts or FP&A roles. Confirm both usability and recovery: an authorized analyst should read the approved baseline, an unauthorized account should not alter it, and the recovery owner should restore a separately held copy without depending on the protected folder. Preserve unexpected behavior before changing controls.
Keep the claim narrow. Local restrictions may reduce accidental writing, deletion or access on a tested Windows path, but they do not encrypt data, establish formula accuracy, approve assumptions, validate forecasts, prove accounting compliance, administer identities, provide version history or replace backup. Escalate those requirements to the spreadsheet, planning and governance systems designed to meet them.
Ask a second analyst to follow the written procedure without verbal help. Record whether that person can identify the approved baseline, create a working copy, recognize the version ID, interpret denied access and find the recovery owner. This usability check reveals ambiguous paths, hidden linked-data dependencies and undocumented knowledge before a spreadsheet, planning, storage or staffing change. Correct the procedure, repeat the test with fictional data and retain only minimal evidence.
04 / BOUNDARY
State what the control cannot prove
Folder Protect is not encryption, model validation, assumption approval, identity governance, spreadsheet access control or proof that another copy does not exist.
Validate the exact Windows account, spreadsheet application, linked-data workflow, storage path and current product release. If encryption, formula validation, assumption approval, immutable history, identity governance or regulated retention are required, select systems designed for those jobs rather than broadening a desktop restriction claim.
05 / SOURCES
Primary references
References support specific controls and do not imply endorsement.